We may earn a commission if you buy through links on this page. It never changes a score or a ranking. How we make money
The bottom line
Invicti unifies code and runtime scanning; confirm API coverage, deployment, and price before committing.
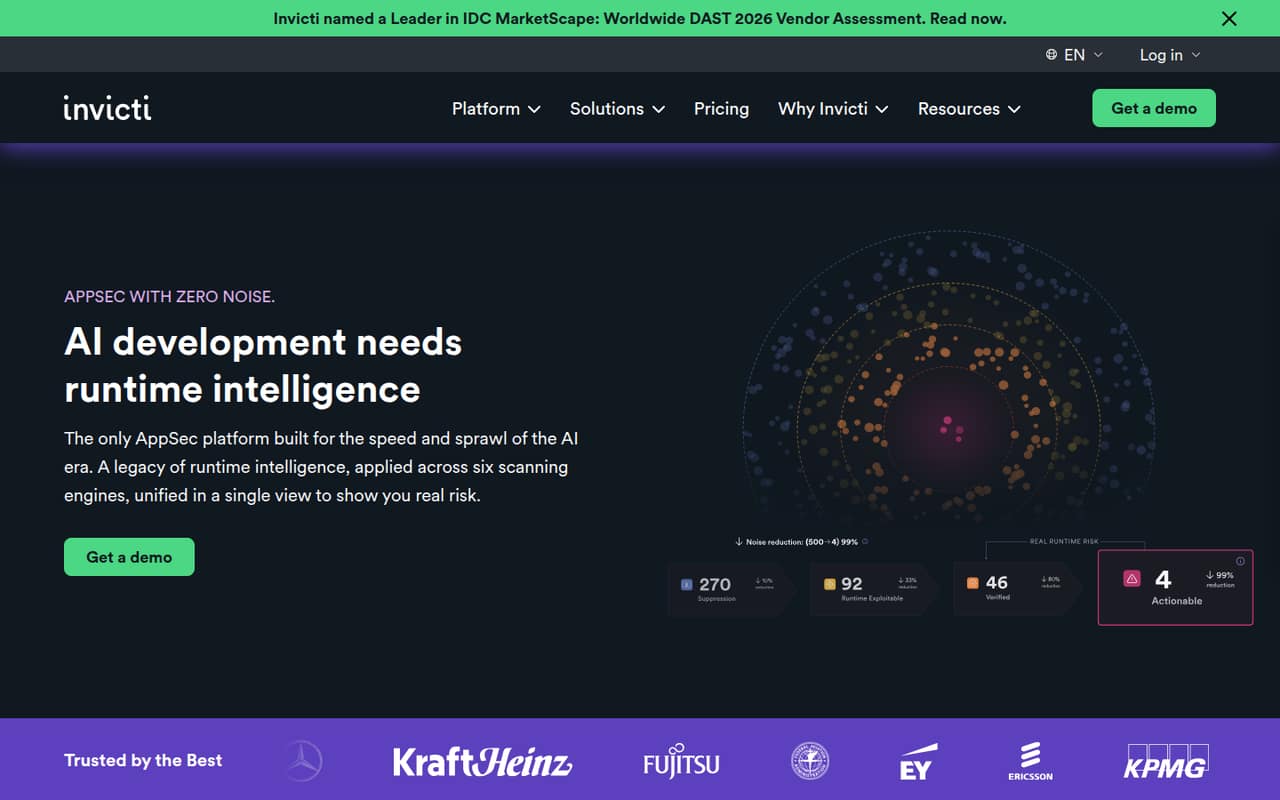
Invicti combines DAST, SAST, software composition analysis, IaC and secrets scanning, and vulnerability management in one AppSec platform. Its core distinction is connecting static findings to runtime reachability and verified vulnerabilities, with proof-based testing for live applications and APIs.
The breadth may suit teams consolidating security findings, but API discovery and testing workflows deserve a proof of concept. Reddit reports are mixed: one team praised it for a Java front end, while others described limited GraphQL results and API workflow friction. Subscription prices are not published.
Good fit if
- Teams consolidating AppSec findings
- Web application DAST programs
- Organizations needing on-prem deployment
Skip it if
- Teams needing published subscription prices
- API-first teams without a proof of concept
- Projects requiring an open-source scanner
ScoresHow it rates
What works
- Combines code, runtime, and supply-chain scanning
- Proof-based DAST validates reported findings
- Connects static issues to runtime context
- Includes SBOM, license, secrets, and IaC scanning
- AppSec Flex offers on-premises and air-gapped options
What doesn't
- Subscription prices are not published
- No free plan or trial is listed
- SDK, CLI, and API integration details need confirmation
- Reddit users report gaps in GraphQL testing
- Data export and migration details need confirmation
01What Invicti is, technically
Invicti is a commercial AppSec platform for scanning source code, testing live web applications and APIs, and managing vulnerabilities. It combines static analysis with runtime application security testing, software composition analysis, IaC and secrets scanning, container security, and vulnerability management. The platform sits across the development pipeline: it can find issues in code and dependencies, test running applications, and bring findings into a central view.
Its main architectural idea is to connect static findings to runtime reachability, exploitability, code ownership, and business context. For DAST, Invicti says it uses proof-based scanning to validate findings in live applications and APIs. The product includes cloud hosting, while the AppSec Flex plan lists Bring Any Cloud, on-premises, and air-gapped deployment options. That makes deployment choice a plan and architecture question rather than a one-size-fits-all assumption. Teams should confirm which scanners, data flows, and deployment modes fit their existing CI/CD and application environments.
02Invicti API, SDKs and docs
Invicti's developer-facing surfaces include scanning live applications and APIs, API discovery and testing, CI/CD security workflows, and a central vulnerability-management view. The homepage lists DAST, AI DAST, API Security Testing, SAST, SCA, IaC, secrets, and container capabilities. It also says SAST findings can connect to code ownership and remediation guidance, while runtime analysis helps prioritize static issues.
The vendor doesn't publish API protocols, SDK languages, or a CLI in its homepage information. Confirm SDK support, API access, authentication, and automation options in Invicti's documentation before designing an integration. The homepage points users to documentation and describes CI/CD workflows, but does not name specific CI providers, plugins, or webhook interfaces. Reddit users discuss importing API definitions and API discovery; one commenter says their organization had to chase updated OpenAPI specs. That makes spec ownership and refresh automation useful proof-of-concept checks, especially for teams with distributed API development.
03Invicti pricing for developers
The pricing page lists no free plan or free trial, and monthly or annual subscription prices are not published. Agentic Pentest is the one priced offer: it costs up to $500 per pentest and includes delivery within 24 hours, an audit-ready PDF report, validated findings, and remediation guidance.
The subscription plans are Web + API for DAST and runtime validation; AppSec Core for SAST, SCA, IaC, container security, SBOM with VEX, and vulnerability management; AppSec Flex for AppSec Core plus deployment flexibility and additional enterprise features; and Your AppSec for a tailored package. Their monthly and annual prices are not published, so there is no reliable public starting price or way to calculate a bill by scan volume, applications, seats, or usage. Ask Invicti for a quote based on your target inventory, scan cadence, deployment model, and included support. The pricing page lists no add-ons; confirm what is included before budgeting a production rollout.
04Invicti: open source, self-hosting and lock-in
Invicti is sold as a commercial platform; the vendor does not publish an open-source licence for the platform. AppSec Flex lists Bring Any Cloud, on-premises, and air-gapped deployment options, so self-hosting is available as a plan-level deployment choice rather than a general free edition.
The vendor doesn't publish data-export formats or a migration path in its homepage information. Before centralizing findings, ask which records and scan histories can be exported, whether exports include enough metadata to preserve ownership and remediation state, and how long data remains available after cancellation. Lock-in risk depends on how much of your workflow relies on Invicti's correlation, prioritization, and reporting rather than portable scanner outputs. Keep API definitions, asset inventories, and remediation records in formats your team can retain independently.
05Invicti in production
Invicti's production value depends on coverage and integration fit, not just the number of scanner types. Before rollout, validate authenticated scans, API-definition handling, scan scheduling, CI/CD behavior, finding ownership, and the effect of proof-based testing on your applications. Ask the vendor about rate limits, concurrency, scan-time limits, service availability, data retention, and the security controls available for your chosen deployment; these can affect operational planning.
Reddit reports are mixed. One commenter said Invicti worked well for their Java front end. Other developers described limited results for a growing set of GraphQL APIs, difficulty identifying API owners, and friction around keeping OpenAPI specs current. Those are individual reports, not universal product limits, but they point to concrete proof-of-concept cases. Test representative APIs and authenticated workflows, and establish who maintains API definitions before depending on scan coverage for release decisions.
From the threadsWhat users say
Reddit sentiment is mixed. One team praised Invicti for a Java front end, while other commenters raised API coverage and ownership concerns.
we're a Java front end which Invicti rocks
The results we get for our GraphQL APIs are very limited, and their number is rapidly scaling internally
it doesn't do the work
The biggest problem with Invicti for us is indeed on the API side, and we can't have a separate API scanner at the moment
Questions people ask
What does Invicti do?
Invicti is an AppSec platform that scans code, tests live web applications and APIs, and manages vulnerabilities. Its features include DAST, SAST, software composition analysis, IaC and secrets scanning, container security, and vulnerability management. It also connects static findings to runtime reachability and exploitability to help prioritize remediation.
Does Invicti use AI?
Yes. Invicti's homepage lists AI DAST and AI AppSec. It also describes Octo as a hybrid agentic pentester combining scanners and AI, with audit-ready reports in under 24 hours for $500 or less per pentest. Confirm which AI features are included in the plan you are considering.
Can Invicti scan APIs?
Yes. Invicti lists API Security Testing and DAST for running web applications and APIs. A Reddit commenter says API definitions can be imported for scanning, while others report limited GraphQL results and difficulties with API ownership and keeping OpenAPI specs current. Validate your own API types and workflows in a proof of concept.
Can Invicti run on-premises?
AppSec Flex lists Bring Any Cloud, on-premises, and air-gapped deployment options. The Web + API plan lists cloud hosting. Ask Invicti which deployment modes are available for the scanners and management components you need, and confirm related infrastructure and support requirements before purchase.
How much does Invicti cost?
Agentic Pentest is listed at a maximum of $500 per pentest. The pricing page does not publish monthly or annual subscription prices for Web + API, AppSec Core, AppSec Flex, or Your AppSec. There is no listed free plan or free trial, so request a quote for your application inventory and deployment needs.