We may earn a commission if you buy through links on this page. It never changes a score or a ranking. How we make money
The bottom line
Broad application-risk coverage, with custom pricing and key integration details to confirm before committing.
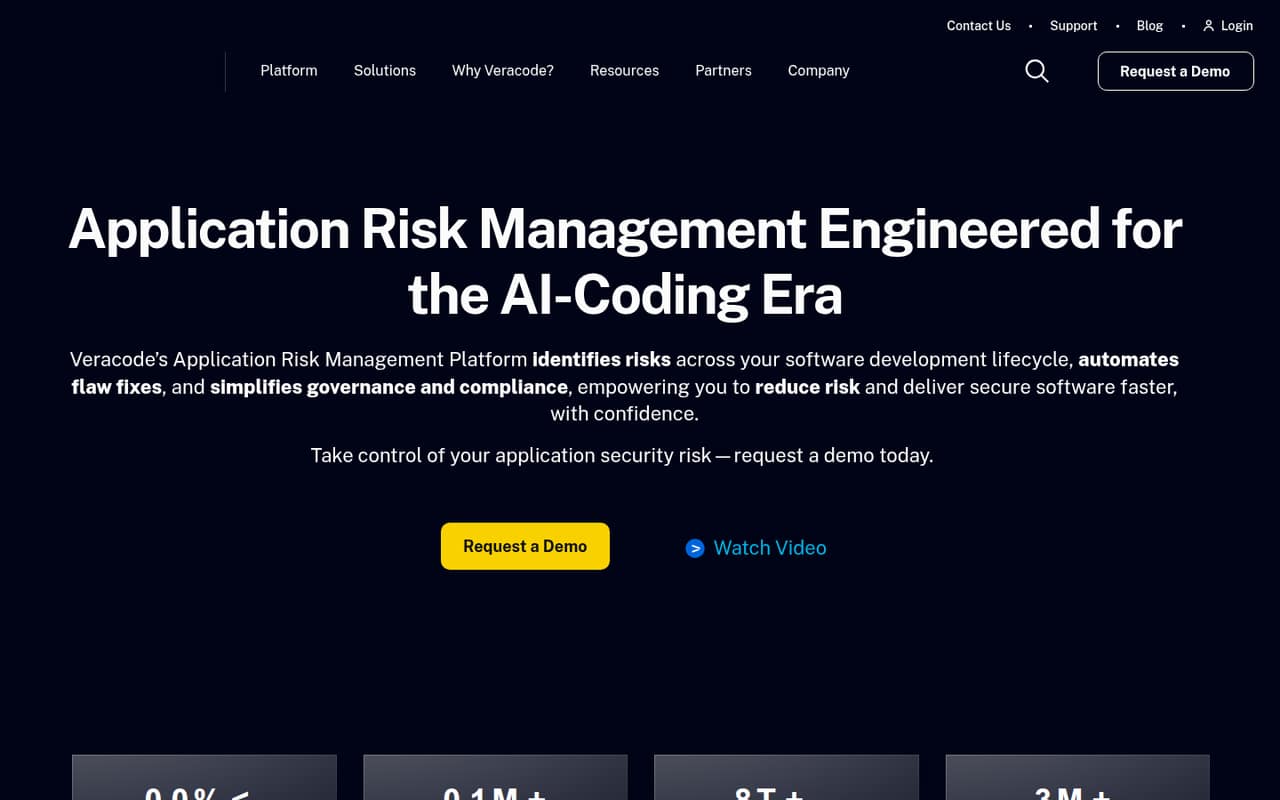
Veracode is a commercial application-risk platform for security teams, developers and organizational leaders. It covers code, dependencies, containers and runtime signals, with remediation guidance, AI-driven fixes and governance features.
The homepage describes integrations into existing developer workflows, but does not name API protocols, SDKs, languages or a CLI. The pricing page lists custom enterprise quotes, with no published starting price. Reddit feedback is sharply critical overall, though one commenter says their organization has used Veracode for years.
Good fit if
- Enterprise security and governance teams
- Teams seeking centralized risk visibility
- Organizations evaluating AI-assisted fixes
Skip it if
- Teams requiring published, self-serve pricing
- Projects requiring documented SDK support
- Organizations requiring on-prem deployment
ScoresHow it rates
What works
- Covers code, dependencies, containers and runtime signals
- Includes AI-driven remediation and flaw fixes
- Targets governance, reporting and policy control
- Positions guidance and fixes inside existing tools
- Supports security across the SDLC and supply chain
What doesn't
- Enterprise pricing is custom and not published
- Homepage does not name SDKs, languages or API protocols
- No free plan or trial is listed
- A Reddit user reports historical dashboard metrics changed
- Reddit commenters report inconsistent support and scan results
01What Veracode is, technically
Veracode is a commercial application-risk management platform, positioned as a hosted service rather than a library or CLI. A Reddit commenter describes it as cloud based; confirm deployment options with Veracode if your environment requires on-premises scanning. The platform sits across the software development lifecycle, aiming to give security teams and leaders visibility into application risk while giving developers remediation guidance and AI-driven fixes.
The homepage says it covers code, dependencies, containers and runtime signals, and supports supply-chain security, governance and compliance. That makes it an application-security layer alongside development workflows, rather than a general-purpose code-hosting or runtime platform. Veracode says it identifies risks and automates flaw fixes, but the homepage does not define the specific scan inputs, deployment architecture or data flow. Verify those details for your build pipeline, especially if source code or artifacts cannot leave your environment.
02Veracode API, SDKs and docs
Veracode's homepage describes developer guidance and AI-driven fixes inside the tools developers already use, plus security practices and tools integrated across the SDLC. It does not name the integration mechanisms behind that workflow. The homepage names no API protocol, SDK, programming language, CLI, webhook or plugin. Veracode does not publish those integration details on the homepage, so confirm SDK support and integration options in the vendor's docs before designing an implementation.
Ask whether the workflow you need uses a REST API, webhooks, CLI, plugins or another mechanism, and check support for your language, CI system and code host. Also confirm which artifact the scanner consumes and how findings and fixes return to developer tools. The vendor describes automated fixes and remediation guidance, but publishes no technical setup sequence or compatibility matrix on the homepage. Treat a demo as a chance to validate your actual pipeline, not as proof of a specific integration.
03Veracode pricing for developers
The pricing page lists custom enterprise quotes and publishes no monthly or annual price. There is no published starting price, standardized plan tier, free plan or free trial. The listed route to pricing is to request a demo or contact sales. Billing terms are not published.
The page also publishes no seat, usage or scan limits, and no pricing formula tied to requests, compute or application count. As a result, we cannot estimate how a bill changes as a team adds developers, projects or scan volume. No add-ons are listed in the pricing information. Before procurement, ask for a written quote that defines the included applications, users, environments and scan volume, as well as overage rates, renewal terms and any charges for support or integrations. Without those terms, comparing Veracode’s cost with a usage-priced service or an internally hosted tool is difficult. Treat the price as unknown until sales provides a scoped quote.
04Veracode: open source, self-hosting and lock-in
Veracode is presented as a commercial platform, not as an open-source package. Its homepage does not state a software license or describe source availability. A Reddit commenter calls the product cloud based and says an on-premises requirement would rule it out; confirm the current deployment options with Veracode before sending code or artifacts to the service.
The homepage also does not describe data export or a migration path. Ask how to export findings, policies, scan history and reporting data in usable formats, and whether exports remain available after a contract ends. The platform's centralized reporting and policy controls may become part of security operations, so migration effort depends on what data and workflows can leave with you. Get the export terms and retention period in writing before relying on Veracode as the system of record for application-risk history.
05Veracode in production
Before depending on Veracode in a production pipeline, confirm scan inputs, supported build environments, concurrency, rate limits, scan-size limits, service availability commitments and data-retention terms. The homepage publishes none of those operational limits. Ask how failures and delayed scans surface in CI, and whether teams can keep releases moving when the service is unavailable.
Reddit feedback raises two specific concerns: one commenter says dashboard historical numbers changed over time, and another reports support struggled with basic questions and describes inconsistent results. These are individual reports, not guarantees of how every deployment behaves, but they justify checking how findings and historical metrics are versioned. Reddit commenters also describe Veracode as scanning binaries rather than source; verify the required artifact and data flow with the vendor. Test representative projects and agree on support response expectations before making it a release gate.
From the threadsWhat users say
The Reddit discussion is mostly negative, with complaints about scan quality, reporting consistency and support. A smaller counterpoint is that one commenter says their organization has used Veracode for years, while another sees binary scanning as useful when source must stay private.
Veracode scans binaries, not source, so if that's a requirement you can rule it out
Their entire metrics collection "dashboard" actively changes your historical numbers over time, support struggles to answer basic questions, and it's painfully inconsistent
we’ve been using it for years!
they don't scan source code, they scan binaries, so your source never hits their systems
Questions people ask
How much does Veracode cost?
The pricing page lists custom enterprise quotes, but no monthly or annual price, starting price or standardized tiers. It also publishes no seat or usage limits. Ask sales for a quote that states included applications, users, scan volume, overages and renewal terms before comparing costs.
Does Veracode offer a free plan or trial?
The pricing information lists no free plan and no free trial. The stated purchasing route is to request a demo or contact sales. Ask whether Veracode can provide an evaluation arrangement for your projects and clarify any limits, duration or data-handling terms before starting.
What APIs, SDKs or languages does Veracode support?
The homepage does not name an API protocol, SDK, programming language or CLI. It describes remediation guidance and AI-driven fixes inside the tools developers already use. Check Veracode's technical docs or ask its sales team which integrations and language workflows are supported for your codebase and CI system.
Can Veracode scan source code without uploading it?
Reddit commenters describe Veracode as scanning binaries rather than source, including one who says this keeps source off the vendor's systems. That is user-reported information, not a deployment guarantee. Confirm the accepted artifact, data flow, storage and retention terms with Veracode for your specific scanning setup.
Can Veracode be self-hosted?
A Reddit commenter describes Veracode as cloud based and says it would not suit an on-premises requirement. The homepage does not detail deployment choices. If self-hosting or on-premises processing is mandatory, confirm the current options and where code, artifacts, findings and telemetry are processed before procurement.